
Android EMM Default Policy and Compliance Scope
What
The Android Default Policy defines global baseline settings for managed Android EMM applications and devices. Use scoped Android Policy Filesets for settings that depend on enrollment type, device role, or a specific application.
The practical split is:
- Android Default Policy: Fleet-wide application and device baselines.
- Android Policy Filesets: Controls assigned to the applicable BYOD, fully managed, or Dedicated Device scope.
- Android app Fileset Properties: App-specific overrides when one application needs different behavior from the global default.
When/Why
Use the Default Policy for settings that should apply consistently across the Android fleet. Keep enrollment-specific compliance and operational behavior in separately scoped Policy Filesets so an incompatible setting is not pushed to the wrong device mode.
Do not use the Default Policy as a dumping ground. A global baseline should be safe for every Android EMM device in scope. Use a targeted Policy Fileset when BYOD, Dedicated Device, or app-specific behavior differs.
Open the Android Default Policy in FileWave 16.4
To verify policy changes, use a test device enrolled through Android Enrollment. Test the enrollment modes you intend to manage; a BYOD work profile and a fully managed device are not interchangeable tests.
- Open FileWave Central > Preferences.
- Select Google.
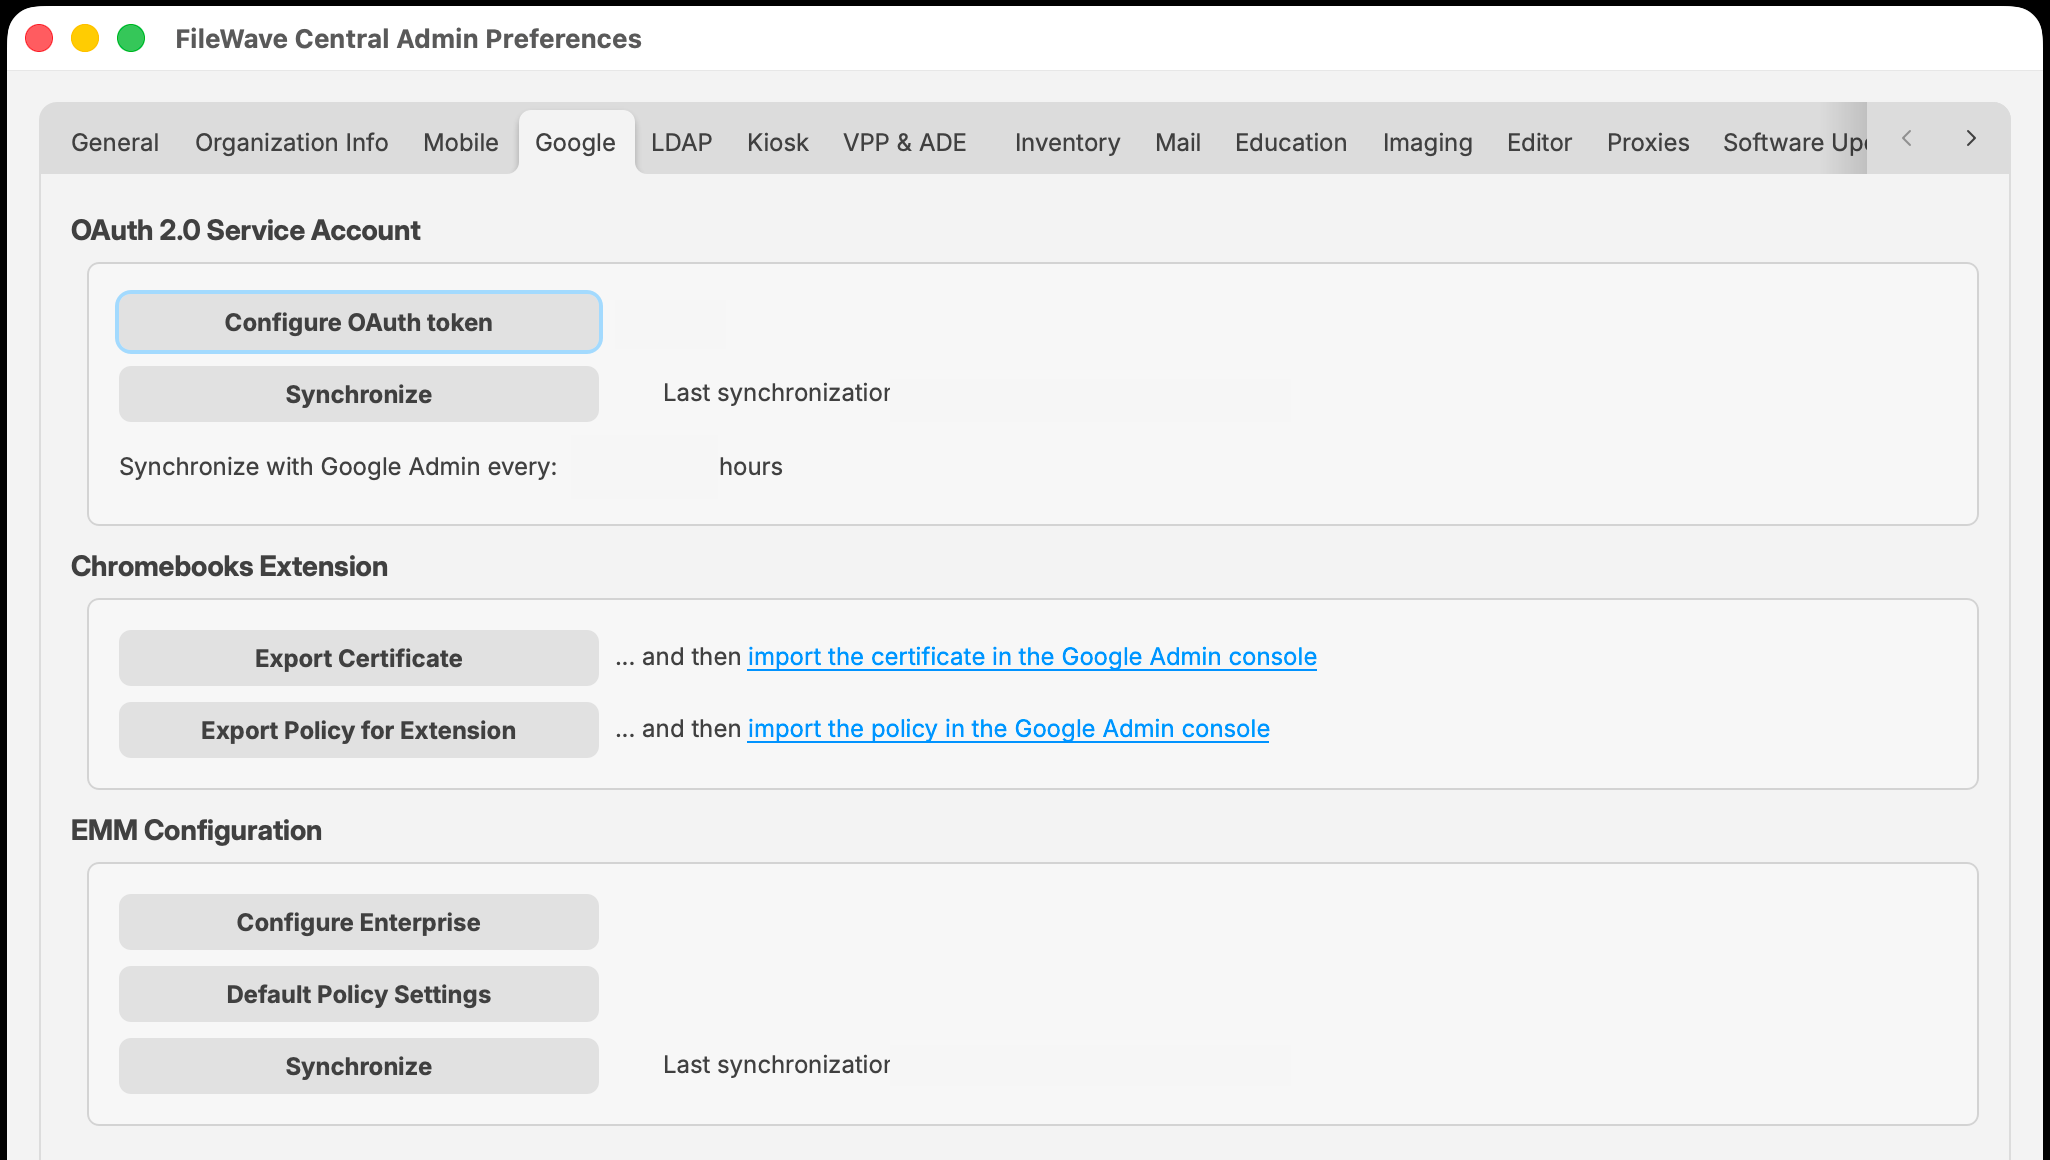
- Under EMM Configuration, select Default Policy Settings.
- Enable Customize default policy when you need to define FileWave-managed defaults.
- Review the values and save the Default Policy. Before updating the model, coordinate with other administrators: a Model Update publishes their pending changes too. The Default Policy is a global baseline, not a pilot-only assignment. Then update the model.
Global application baselines
| Control | Current behavior | Override |
|---|---|---|
| Permission Policy | Defines the default response when an app requests a managed permission. | Permission Policy Filesets and app-specific permissions can provide narrower behavior. |
| Credential Provider Policy | Controls whether apps can act as credential providers on Android 14 and later. The default does not allow this. | Allow only an approved credential-management app through its app Fileset Properties. |
| Android Factory Reset Protection | Registers the managed Google account used to recover a device after a protected wipe and provides access to the FRP email template. | Use a controlled organizational recovery account rather than a personal administrator account. |
| USB Data Access | Defines the global Device Connectivity behavior for files or data transferred through USB. | Use a scoped Policy Fileset when a particular device role requires different USB behavior. |
Auto Update Mode is configured on the Android app Fileset, not in this Default Policy Editor. See Android Apps for the four per-app modes.
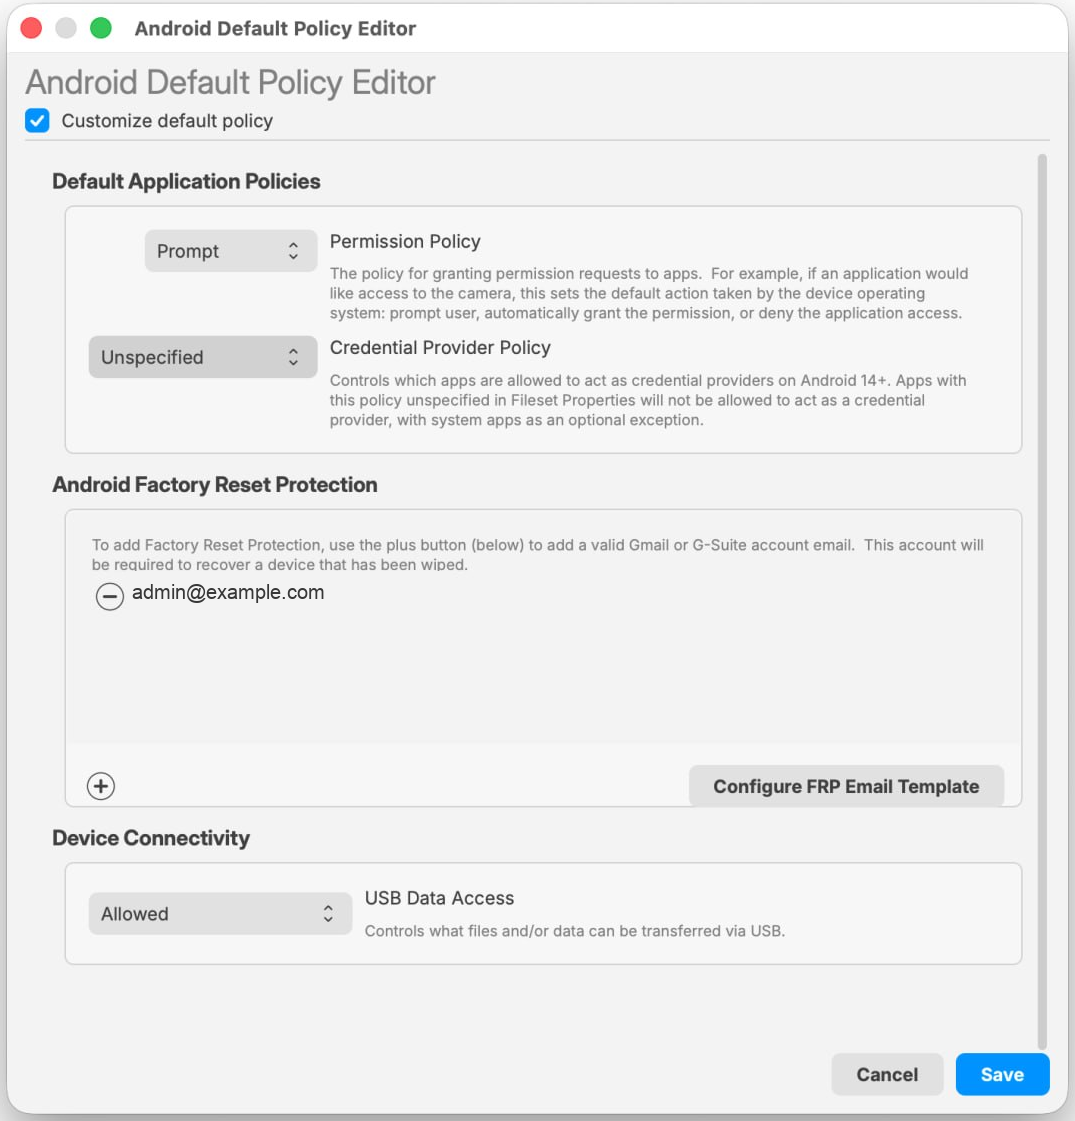
Factory Reset Protection account: Use a managed recovery identity that remains accessible to the organization. Do not tie fleet recovery to an individual employee’s personal Google account.
Scope Password and Keyguard compliance
FileWave 16.4 makes the Password and Keyguard sections optional in an Android Compliance Policy. Build the Policy for the enrollment mode rather than including every available section.
| Device scope | Recommended Compliance Policy design |
|---|---|
| BYOD/work profile | Use Password compliance without Keyguard. Android BYOD is not compatible with the Keyguard component used for Dedicated Device or single-app operation. |
| Fully managed device | Include the Password controls required by organizational policy; add other applicable sections only when needed. |
| Dedicated Device/single app | Include Keyguard only when that device-mode behavior is required. |
Recommended policy pattern
- Keep global application defaults conservative and broadly applicable.
- Use a dedicated BYOD Password Compliance Policy without Keyguard.
- Use a separate Dedicated Device Compliance Policy when Keyguard is required.
- Keep System Update behavior in its own Policy so maintenance windows and Freeze Periods can change without disturbing compliance.
- Configure Auto Update Mode on each Android app Fileset. Use app-specific Credential Provider overrides only for documented exceptions.
- Avoid assigning multiple Policies that manage the same setting differently.
Verify the effective policy
If an app’s permission behavior differs from the global default, check the permission priority: an explicit permission for that app takes priority over a permission configured for all apps in a Policy Fileset, then the app’s default permission, then the global default. Changing the global default does not replace a more specific permission setting.
After the device communicates, open its Device Details in FileWave Central and review Installed Policy for the merged policy, as shown in Android devices with multiple policies. Compare the effective values with the intended enrollment mode and app settings, then check the relevant behavior on the device. A saved Default Policy or successful Model Update alone is not proof that a device applied the setting.
No comments to display
No comments to display