
macOS Privacy Preferences Payload
Description
The classic Privacy Preferences payload requires User Approved MDM.
The Privacy Preferences payload controls the settings that are displayed in the ”Privacy” tab of the ”Security & Privacy” pane in System Preferences. This forms part of Apple's security framework: Transparency Consent and Control (TCC).
PPPC profiles and FileWave Kiosk location access are different workflows. This article covers classic Privacy Preferences Policy Control (PPPC/TCC) profiles. On macOS 26 and earlier, these profiles cannot pre-approve location access for FileWave Kiosk. After upgrading to FileWave 17.0, a logged-in user must approve Kiosk; an earlier fwGUI approval does not transfer.
For supervised Macs on macOS 27 or later, FileWave 17.0 provides a separate, automatic privacy-permissions declaration for its own apps. It still requires user consent and is not a replacement for every PPPC profile. For optional location reporting, follow Location Tracking Setup rather than using the Screen Sharing example below to configure Kiosk.
Admin-configured App Settings in FileWave 17
For supervised Macs running macOS 27 or later, FileWave 17.0 also provides App Settings in the Central DDM Configuration editor. Its app privacy defaults are a separate workflow from the classic PPPC profile instructions below. Privacy defaults do not bypass user consent.
- Choose the Mac user channel. On the DDM Configuration's General page, set Installation to User Scope for app privacy defaults. macOS ignores these privacy settings in a system-scoped configuration, even when the declaration reports valid and active.
- Identify the app correctly. In App Privacy Defaults, each entry needs a unique App Identifier, an Organization Justification and at least one configured permission. On macOS, use
Bundle-ID {Designated-Requirement}, not a bare bundle ID orBundle-ID (Team-ID). The bundle ID before the braces identifies the application; the requirement inside them matches its code signature. This is not the separate BundleID/Path and Code Requirement entry used by classic PPPC. - Keep execution rules separate. On macOS, allowed/denied binary rules and
AlwaysAllowManagedAppsneed System Scope. If you need these as well as privacy defaults, use separate configurations. A binary execution rule is not a grant of privacy access.
Retain classic PPPC profiles for the controls you still need; do not treat App Settings as a replacement for every privacy payload or configure contradictory policies for the same setting. After delivery, check the app's requested access and the user's consent outcome, not just the declaration status. These operating-system access controls are separate from vendor-specific managed app configuration values.
Ingredients
- A supported FileWave release
- macOS 10.14+
- macOS UAMDM enrolled device
FileWave Supported Version
The classic PPPC procedure below is separate from the FileWave 17.0 App Settings workflow above. Check the platform and enrollment requirements of the control you intend to use before deployment.
BundleID or Path
When building TCC Privacy Payloads there are two choices:
- BundleID
- Path
Items within bundles (.app or .bundle), must refer to the bundle and not the path. Otherwise, 'Path' should be selected.
Directions
- Create a New Profile Fileset
- Choose Payload
- Select 'Privacy & Security' in the sidebar
- Select the Privacy tab
- Provide either the App Path or Bundle ID as required and click on the '+'
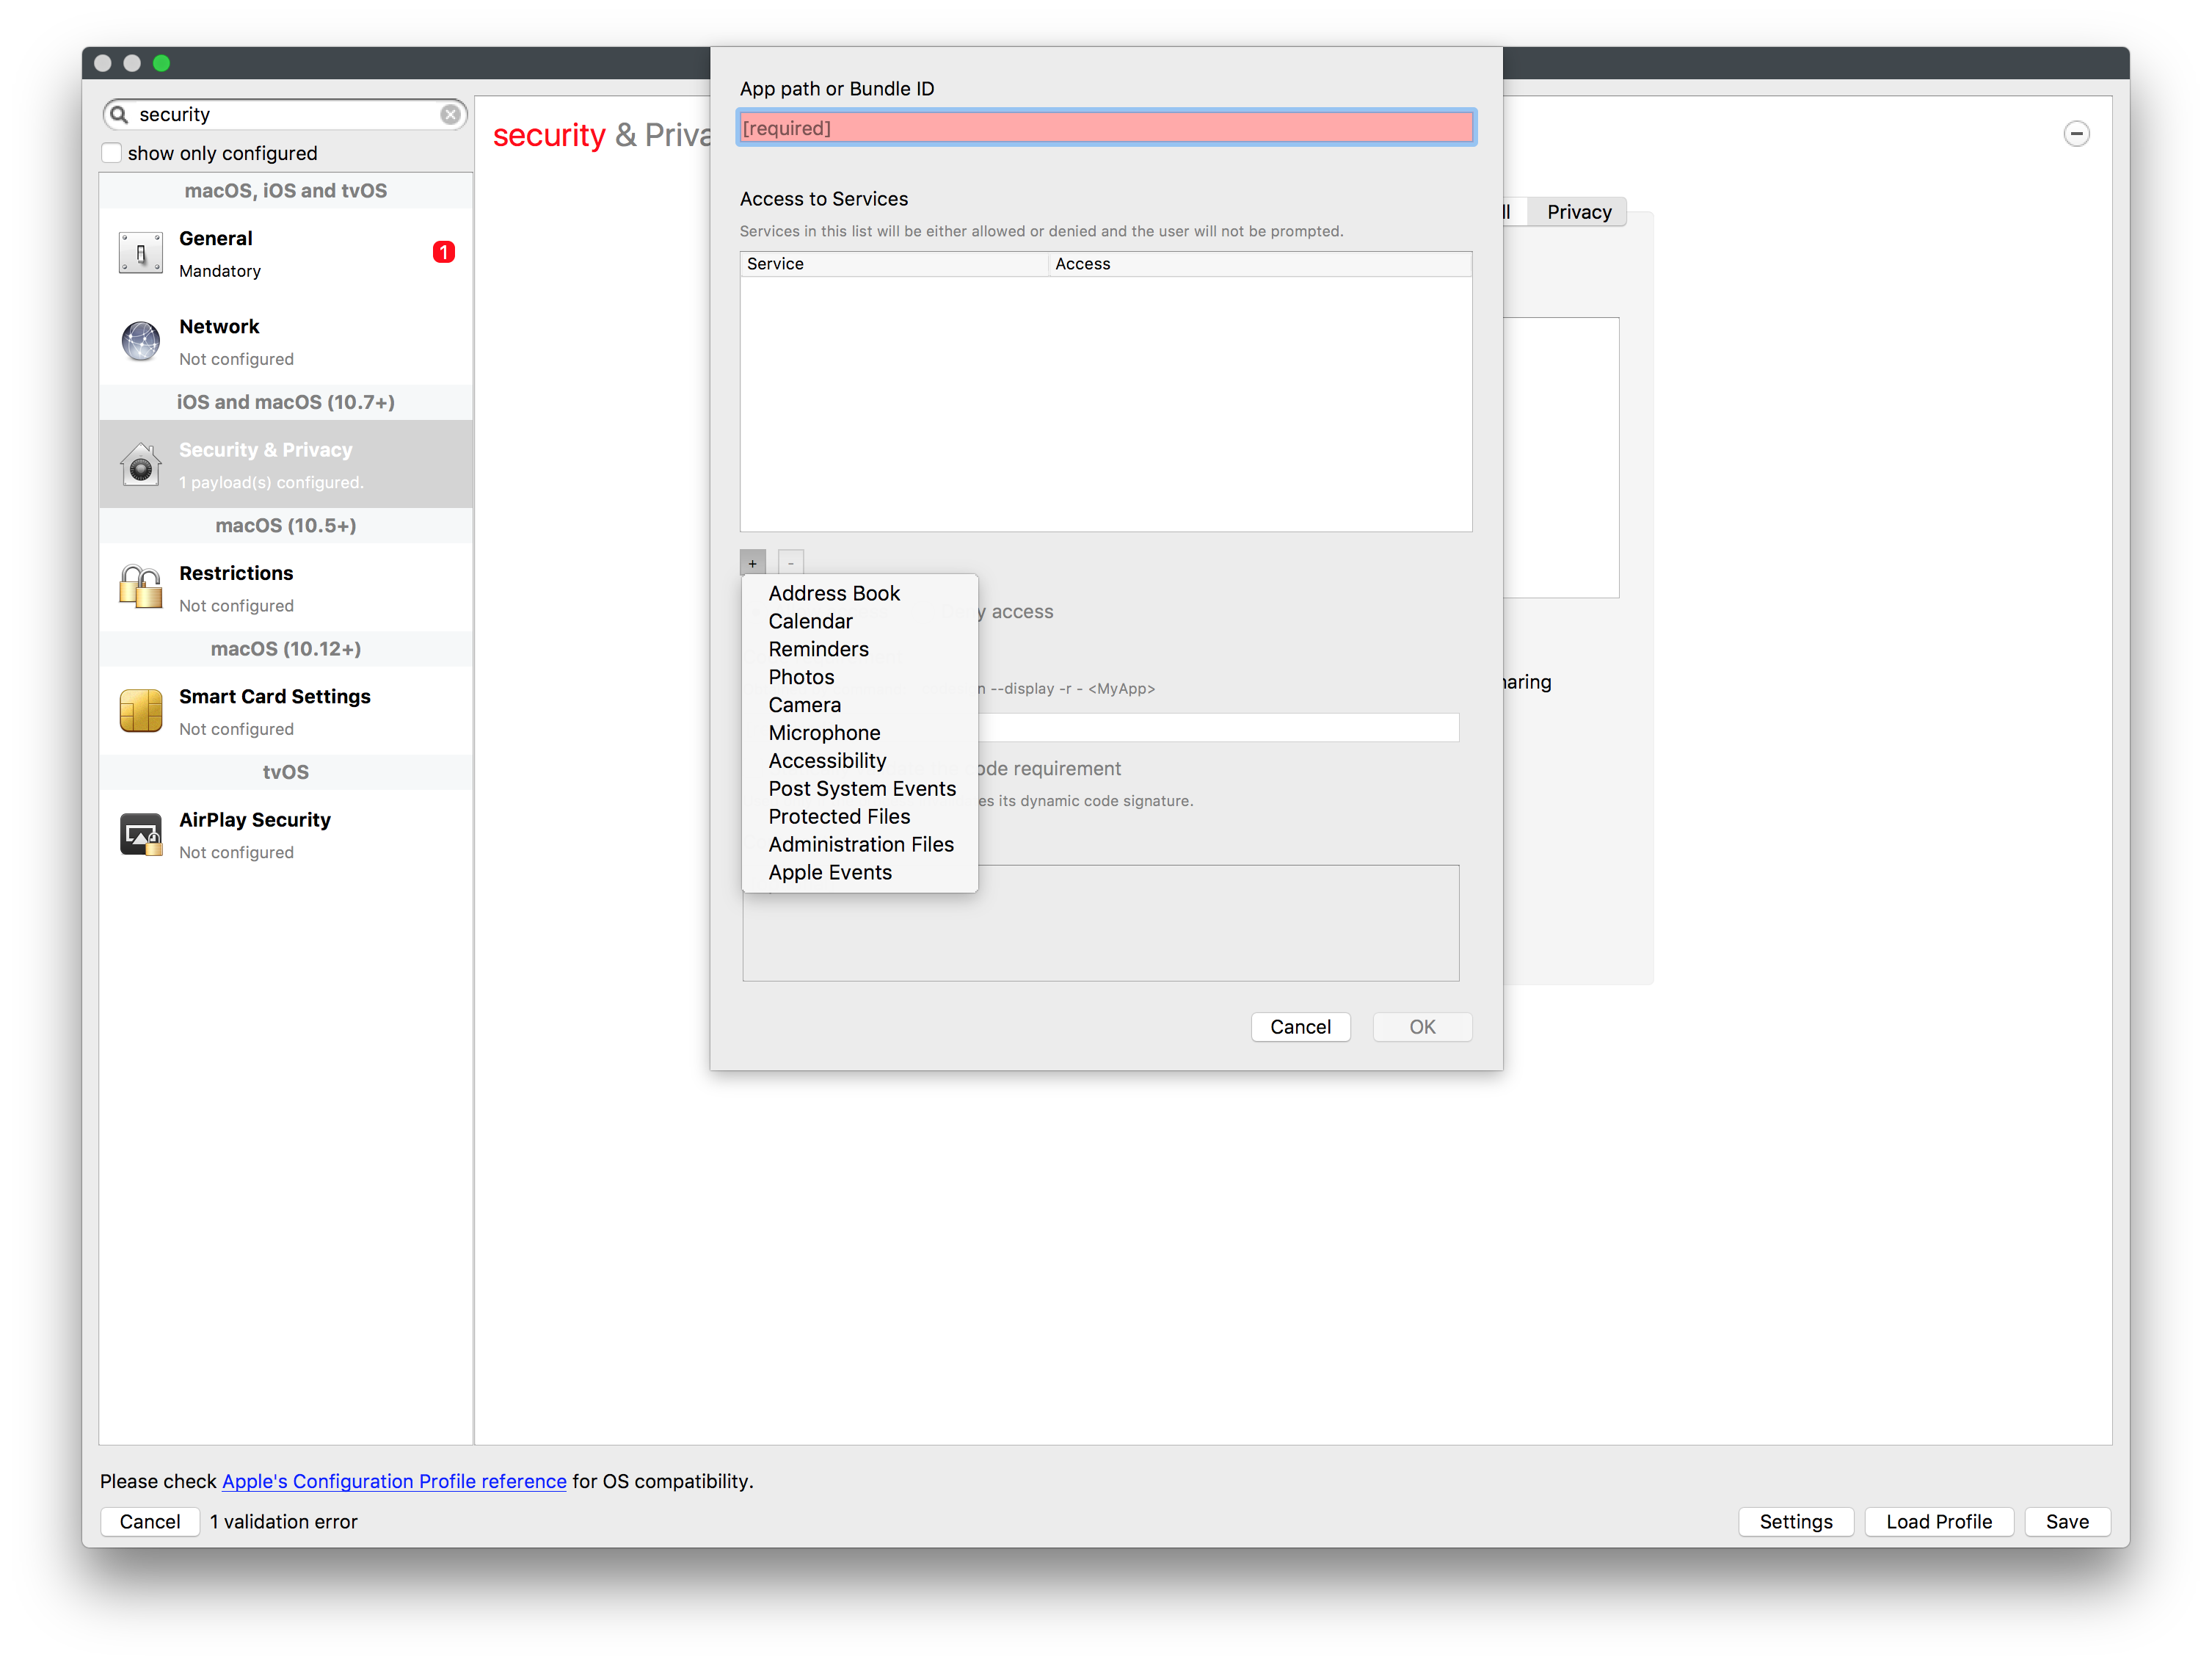
- Choose the necessary Service type
- Add the Code Requirement
Code Required To obtain the required code, as shown in the window the displayed 'codesign' command will need to be run, pointing to the path of either the binary or Application. See below: Requesting Application.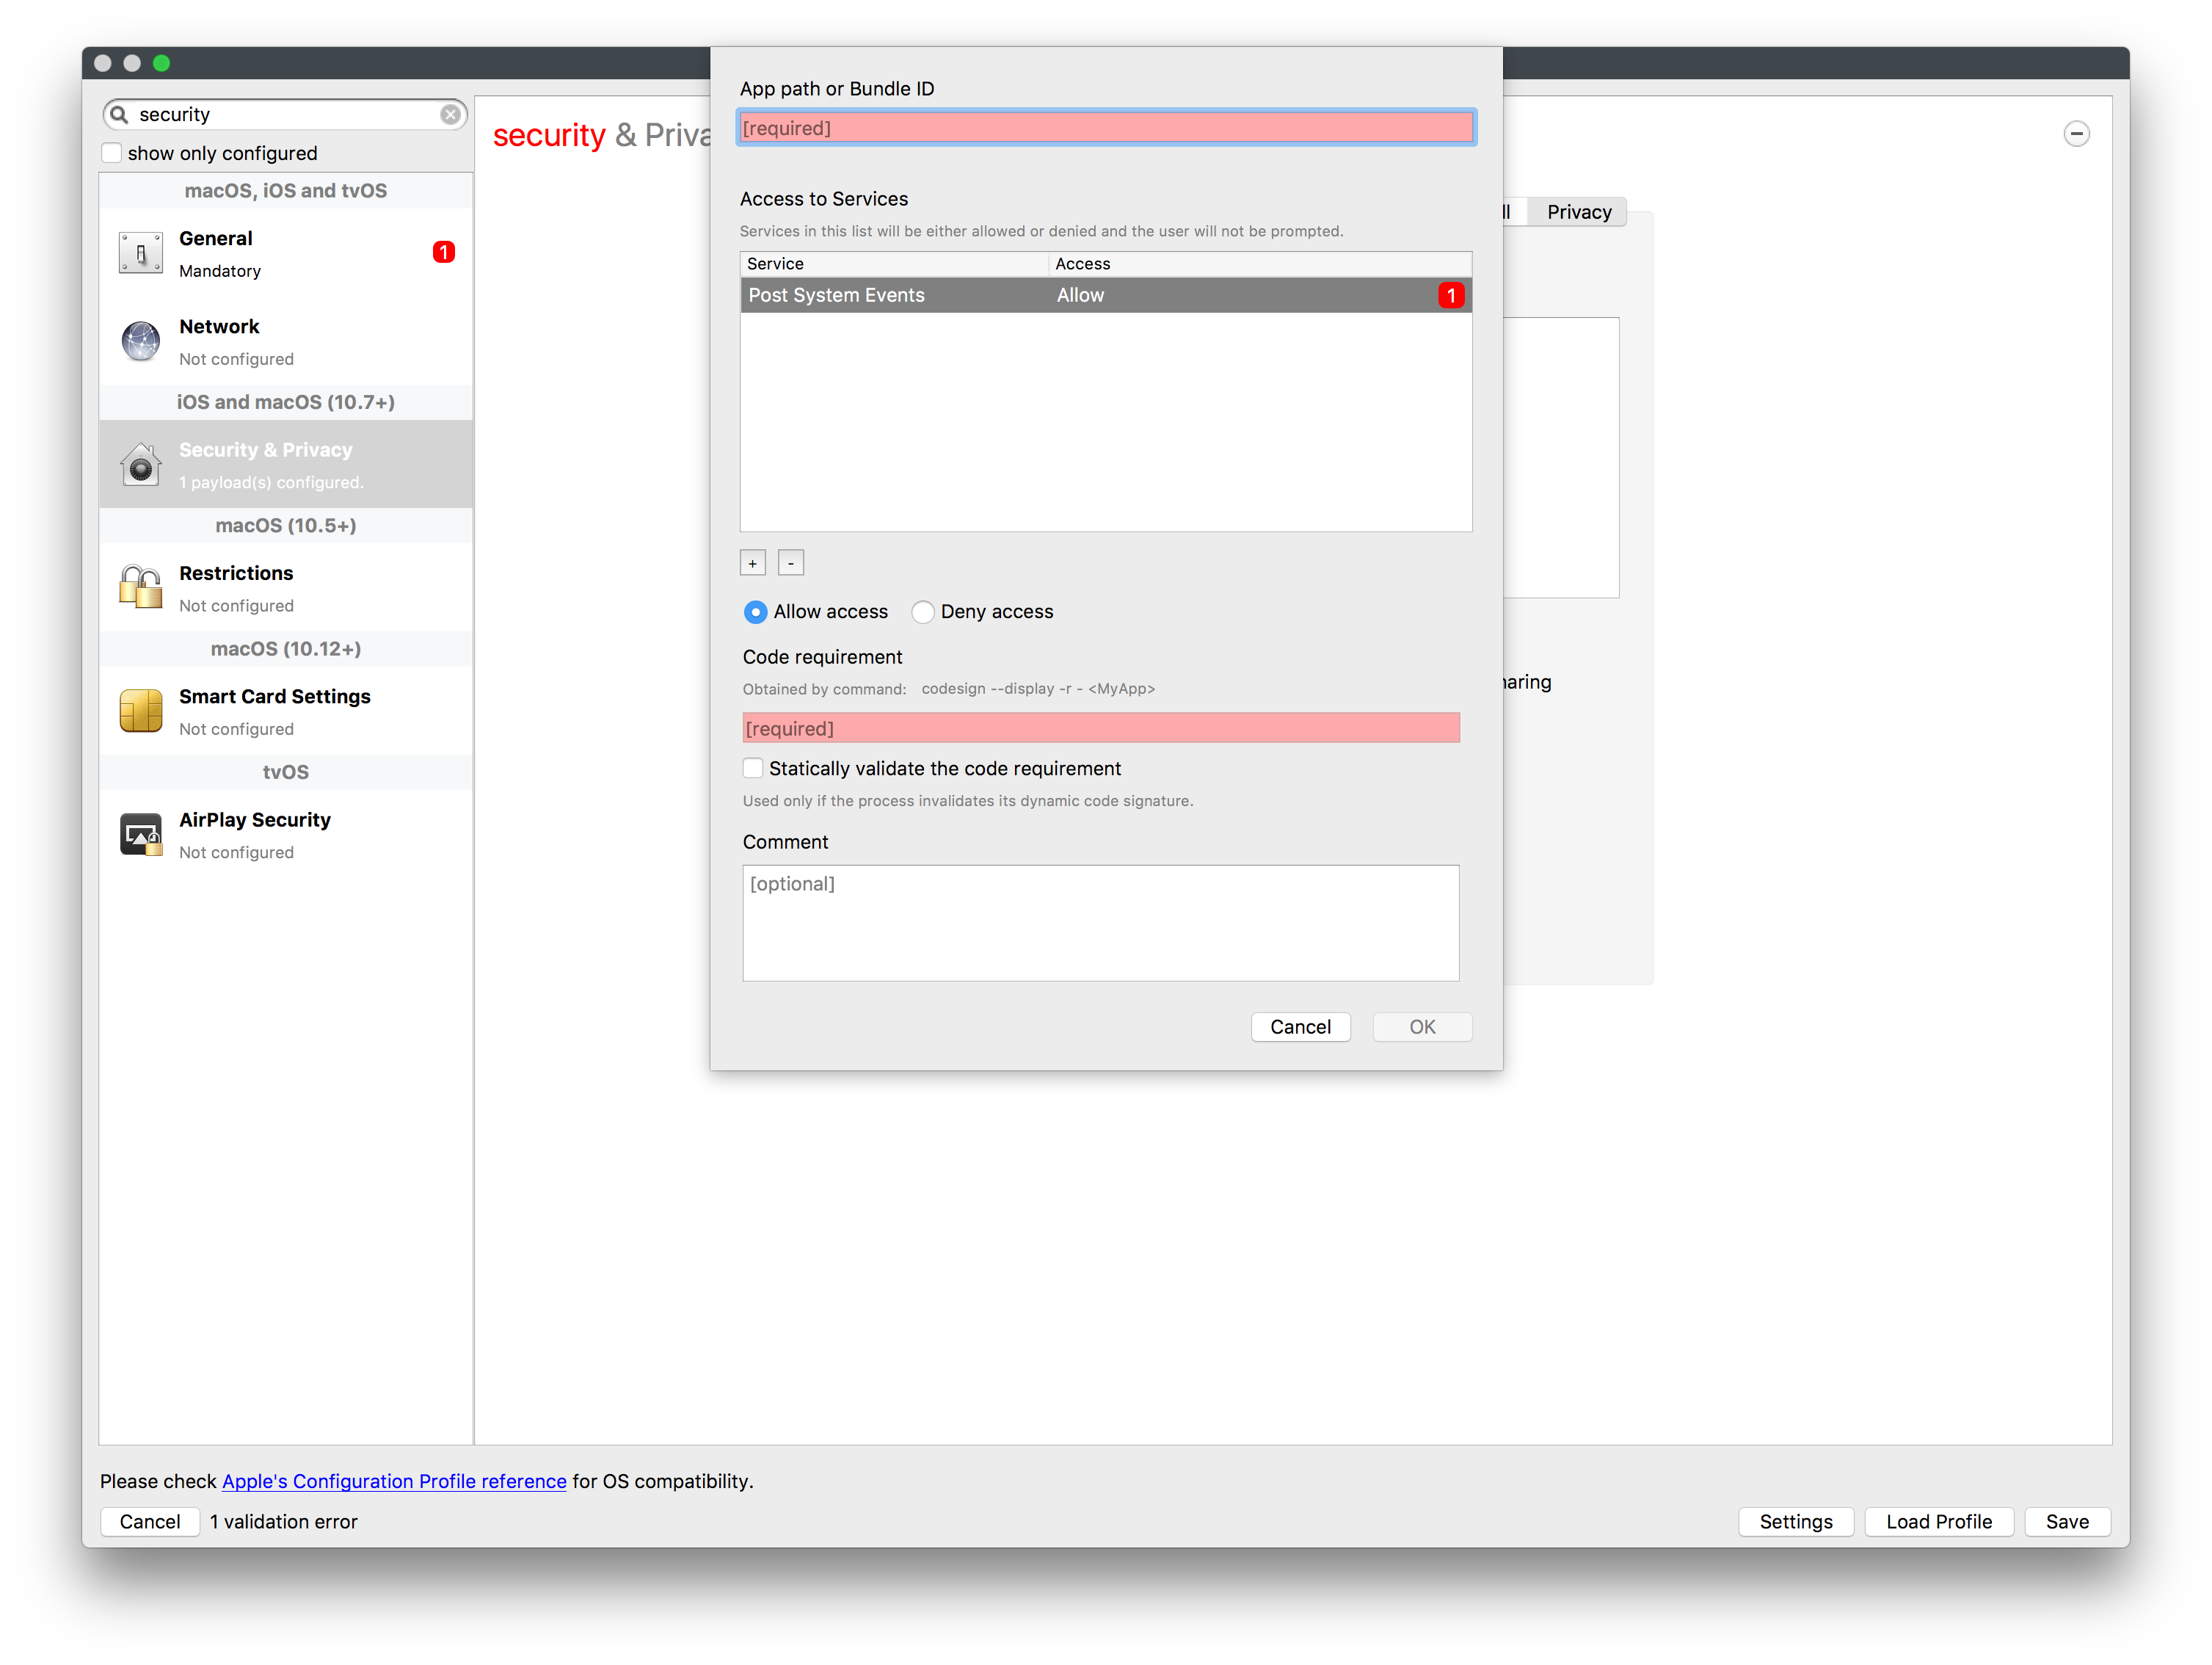
- Set other settings appropriately.
- Save, Associate, and Update Model

System Preferences
When a payload is set to configure a service on a macOS device, the System Preferences view will not reflect this setting, despite it being managed.
Identifying Accessing Service
Run a 'log stream' command on the destination device and then attempt to push the Fileset. Using the following command, the requesting App may be identified:
$ /usr/bin/log stream --debug --predicate 'subsystem == "com.apple.TCC" AND eventMessage BEGINSWITH "AttributionChain"'
Filtering the log data using "subsystem == "com.apple.TCC" AND composedMessage BEGINSWITH "AttributionChain""
Timestamp                       Thread     Type        Activity             PID    TTL
2019-04-04 09:17:22.668813+0100 0x14c8f    Info        0x2a2c2              209    0    tccd: [com.apple.TCC:access] AttributionChain: RESP:{ID: com.filewave.fwcld, PID[8318], auid: 0, euid: 0, responsible path: '/usr/local/sbin/FileWave.app/Contents/MacOS/fwcld', binary path: '/usr/local/sbin/FileWave.app/Contents/MacOS/fwcld'}, ACC:{ID: com.apple.ls, PID[8691], auid: 0, euid: 0, binary path: '/bin/ls'}, REQ:{ID: com.apple.sandboxd, PID[7499], auid: 0, euid: 0, binary path: '/usr/libexec/sandboxd'}
This has shown both the bundle ID and the path to the requesting agent:
# log show --info -last 15m --predicate 'subsystem == "com.apple.TCC" AND eventMessage contains "service="'
Filtering the log data using "subsystem == "com.apple.TCC" AND composedMessage CONTAINS "service=""
Skipping debug messages, pass --debug to include.
Timestamp                       Thread     Type        Activity             PID    TTL
2019-04-04 09:17:22.665903+0100 0x14c8f    Info        0x2a2c2              209    0    tccd: [com.apple.TCC:access] tccd[209](0): handling request from PID[7499](-1): {
	service="kTCCServiceSystemPolicyAllFiles"
	function="TCCAccessRequest"
	preflight=false
	target_token={pid:8691, auid:-1, euid:0}
	background_session=false
}
Profile Services
Apple's list of manageable services:
- Apple MDM Support Privacy Preferences Policy Control List
- Apple Developer Privacy Preferences Policy Control List
Denied Only
Some items only have the option to be denied; allowance is only possible by the user. Examples include:
- Camera (macOS 10.14+)
- Microphone (macOS 10.14+)
- Screen Capture (macOS 10.15+)
macOS 10.5+
Default behaviour of some services is different between macOS 10.14 and 10.15+. The below example is a demonstration of this experience. Testing of each major version of macOS, from 10.14 up, is advised.
Example
Configure FileWave to use Apple's Screen Sharing Application and allow the Apple Screen Sharing Agent.
macOS 10.15+
As of macOS 10.15+ Screen Sharing has been included as a separate service, which may only be denied. Only Users can allow Screen Sharing. However, devices that are UAMDM enrolled, may have Apple's Screen Sharing service enabled and FileWave may be configured to use this service as suggested in the next section along with the following Privacy Payload.
It should be noted, that there are two options when logging in with 10.15+ if the user authenticating Screen Sharing differs from the user currently logged in:
- Log in as yourself (the user name that was used to authenticate the screen sharing)
- Ask for permissions to view the display (user must accept the prompt that will appear on their screen)
It is not possible to configure macOS 10.15+ with permission for Screen Sharing control of a users environment, without the users accepting the request, where a user is logged in that differs from the authenticated Screen Sharing user. However this method offers the option to prompt the user to accept the request; prompting will occur on every new Screen Sharing attempt.
This method with 10.15+ provides both Observation and Control.
Reconfigure FileWave for Apple's Screen Sharing Application
By default, FileWave has its own built-in Screen Sharing Agent. To adapt this, follow the details laid out in Apple's Screen Sharing Application
Prior to macOS 10.14+ this would allow full control of the macOS device. Due to the new TCC Privacy Framework, macOS 10.14+ will only allow observation when using this method and a privacy payload is required.
Privacy Payload to Allow Apple's Screen Sharing Agent
Apple have provided details to allow the Apple Screen Sharing Agent, which provides the necessary information to build the profile. If these details were not provided though, they may be obtained (see 'Requesting Application' below).
For simplicity, use this provided Fileset: Profile - TCC - Screen Sharing.fileset.zip
Deployment
Associate both the Fileset to configure FileWave to leverage Apple's Screen Sharing and the Fileset to allow the Apple's Screen Sharing Agent, Update Model and test client observation.
Requesting Application
Details of the requesting Application can be viewed if need be. On a test client device, run the following command in Terminal:
$ /usr/bin/log stream --debug --predicate 'subsystem == "com.apple.TCC" AND eventMessage BEGINSWITH "AttributionChain"'
This will give a live output of events requesting access. Configure a device to use Apple's Screen Sharing App from above and attempt to run the required Application (in this case use 'Observe Client' from the Admin console) to the test client. The following should be observed on the client:
$ /usr/bin/log stream --debug --predicate 'subsystem == "com.apple.TCC" AND eventMessage BEGINSWITH "AttributionChain"'

Filtering the log data using "subsystem == "com.apple.TCC" AND composedMessage BEGINSWITH "AttributionChain""

Timestamp                       Thread     Type        Activity             PID    TTL
2018-10-12 07:54:39.013089+0100 0xa1b1     Info        0x21eb3              209    0    tccd: [com.apple.TCC:access] AttributionChain: ACC:{ID: com.apple.screensharing.agent, PID[1125], auid: 501, euid: 501, binary path: '/System/Library/CoreServices/RemoteManagement/ScreensharingAgent.bundle/Contents/MacOS/ScreensharingAgent'}, REQ:{ID: com.apple.WindowServer, PID[176], auid: 88, euid: 88, binary path: '/System/Library/PrivateFrameworks/SkyLight.framework/Versions/A/Resources/WindowServer'}
This has shown both the bundle ID and the path to the requesting agent:
com.apple.screensharing.agent/System/Library/CoreServices/RemoteManagement/ScreensharingAgent.bundle/Contents/MacOS/ScreensharingAgent
Using the agent path, the Code Requirement can be retrieved.
$ codesign -dr - /System/Library/CoreServices/RemoteManagement/ScreensharingAgent.bundle/Contents/MacOS/ScreensharingAgent

Executable=/System/Library/CoreServices/RemoteManagement/ScreensharingAgent.bundle/Contents/MacOS/ScreensharingAgent

designated => identifier "com.apple.screensharing.agent" and anchor apple
In this case, the Code Requirement is:
identifier "com.apple.screensharing.agent" and anchor apple
These details may now be used to create a Privacy payload
Identify Accessing Service
The 'log show' command may be used to observe actions that have previously occurred. In this example
# log show --info -last 15m --predicate 'subsystem == "com.apple.TCC" AND eventMessage contains "service="'
Filtering the log data using "subsystem == "com.apple.TCC" AND composedMessage CONTAINS "service=""
Skipping debug messages, pass --debug to include.
Timestamp                       Thread     Type        Activity             PID    TTL
2019-04-04 09:17:22.665903+0100 0x14c8f    Info        0x2a2c2              209    0    tccd: [com.apple.TCC:access] tccd[209](0): handling request from PID[7499](-1): {
	service="kTCCServiceSystemPolicyAllFiles"
	function="TCCAccessRequest"
	preflight=false
	target_token={pid:8691, auid:-1, euid:0}
	background_session=false
}
FileWave Client
FileWave 17.0 removes Accessibility and PostEvent from the automatic FileWave Client privacy profile. If your script Filesets automate the macOS user interface, deploy the supplemental profile before the updated automatic profile reaches those Macs. See Granting Accessibility to the FileWave Client for UI-scripting Filesets. Full Disk Access is separate and remains in the automatic profile.
Starting in FileWave 16.2.3, the FileWave client code signing identity changed from FileWave (Europe) Gmbh (83S2TRZ3CS) to FileWave (USA), Inc. (UWMR88SA8G). When the FileWave Client is deployed via MDM, FileWave 16.2.3 and later automatically updates the deployed TCC profile for fwcld. If you compare older examples or older custom profiles, you may still see the previous team identifier.
Providing access to services to the FileWave Client requires:
- App path or Bundle ID: com.filewave.client
- Code Requirement: identifier "com.filewave.fwcld.pkg" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = "UWMR88SA8G"
No comments to display
No comments to display