FileWave Server Setup
Choose your server route
By the end of this lesson, you will have a FileWave Server you can reach in FileWave Central, with the name, access, and network settings needed for your evaluation. Choose one route; you do not need to install every component.
| Your setup | Start here | Who manages the server? |
|---|---|---|
| FileWave hosts your server | Cloud-Hosted Server | FileWave manages the hosting; you administer devices through Central or supported Anywhere workflows. |
| You will use a dedicated Mac | Self-managed macOS Server | Your server and network administrators. |
| You will use a virtual machine | Debian Server appliance | Your virtualization, server, and network administrators. |
These are new-server instructions. If your evaluation already has a working server, confirm its address and version with its owner and go to FileWave Central Setup. Do not reinstall or upgrade it just to follow this lesson.
A Booster provides optional content caching, and an Imaging Virtual Server (IVS) supports optional Windows imaging. Neither is required to connect to your Server or begin a device-enrollment evaluation.
Cloud-Hosted Server
- Obtain the server's fully qualified domain name (FQDN), FileWave version, and application administrator credentials from your assigned FileWave systems engineer (SE) or implementation contact. An FQDN is the complete server name, such as
filewave.example.com, rather than an IP address. - Confirm the evaluation start and expiration dates. Hosted evaluations are intended to retain your work if you purchase FileWave; confirm how that continuation works, along with hosting charges and service terms, with your contact before the evaluation expires.
- Ask your network administrator to allow the connections needed from your administration computer and test-device network. The port reference separates Central, Client, and platform traffic. Internet access alone does not mean a firewall allows every required connection.
- Follow FileWave Central Setup to install the matching Central version and sign in with the supplied credentials. Confirm that you reached your assigned evaluation environment before changing anything.
You are ready to continue when: Central connects to the expected Server and you can open its administration views. Continue with the relevant Central Preferences and your chosen device platform. You do not need a Model Update just to log in.
If connection fails: confirm the supplied name, version, credentials, and network access with your FileWave contact. Do not try appliance passwords or repeatedly guess a password.
What FileWave hosting takes care of
FileWave manages hosted infrastructure, the standard hosted server name and certificate, backups, and Server upgrades. This reduces your setup and maintenance work. See Cloud Hosting Product Information for the service overview; pricing, availability commitments, and upgrade arrangements depend on your agreement.
Stop here if FileWave hosts your Server. You do not use SSH, Webmin, server installers, or server certificate/file edits from the self-managed sections below. Ask your FileWave contact to coordinate any hosted-server changes.
Before you install a self-managed server
Agree on the network and recovery plan
Work with the administrators who own your network and server. Have these details ready before installation:
- A dedicated evaluation server and an authorized administrator. Keep it separate from an existing production FileWave installation. Agree on who will maintain backups, security updates, power protection, and recovery.
- A stable IPv4 address: either a manually configured static address or, for an appliance, a DHCP reservation tied to its persistent virtual NIC MAC address. Record the address, subnet mask, default gateway, and approved DNS servers. The network owner must prevent address conflicts.
- One FQDN and a DNS record. Have the DNS administrator create the server's A record. Do not use an IP-only identity for enrollment: a name lets you change the server's address later without changing every device's connection settings.
- A trusted certificate for that name. The name must be included in the certificate's Subject Alternative Name (SAN). Have the certificate owner prepare a protected PKCS #12 (
.p12) bundle and its password. See Name and Certificate Planning. Protect the private key and arrange renewal before expiration. - Local or hypervisor console access. Confirm that it works before changing networking. Record existing settings and arrange a recoverable backup or a clean, pre-enrollment VM snapshot. A remote session can disconnect when an address changes; it is not your recovery method.
- Enough resources for your evaluation. Account for the OS, database, Filesets, software-update content, and backups—not only the installer download. Use Server System Requirements for general sizing and the selected release's Server compatibility table for OS support. The older OS list in the general requirements article is not the current release matrix.
Manage devices on and off your network
The same FQDN must resolve correctly from every intended device network, and devices on each network must be able to reach the Server using that name. In a typical setup, internal DNS returns the private server address; external DNS returns the public address whose firewall forwards the required device traffic to that Server. Ask the network owner to verify both paths. A successful connection from the server room does not establish that an off-network device can connect.
Use Default TCP and UDP Port Usage to select rules for your actual components and platforms, including their outbound services. Do not open every listed port. Keep administration access restricted to trusted networks or your approved remote-administration path; do not publish SSH or Webmin port 10000 to the internet. Central uses port 20016 for its main connection and has additional connections listed in the reference.
FileWave Server components should use IPv4 with IPv6 disabled. Current Debian appliances already handle this configuration. The macOS preparation below explains how to check the correct network service before changing it.
FileWave Server Installation
Choose a release and its matching downloads
Start at Downloads. Use the latest generally available release unless your FileWave contact has selected another supported version. Do not choose an Early Access build just because its version number is higher.
The steps below use FileWave 16.4.1:
- macOS Server: choose the Mac hardware and macOS version from the Server compatibility table on the release page. That table distinguishes QA-tested versions from other listed platforms. Do not use the Client requirements for a Server installation.
- Debian Server appliance: use the prebuilt Debian x86_64 Server image and check its release-specific requirements. Do not select the Booster or IVS image.
- Memory: the release lists an 8 GB Server minimum. General guidance recommends 16 GB; agree on CPU and storage sizing with the server owner rather than treating the minimum as a capacity recommendation.
- Virtualization: the Hyper-V image is Generation 2. Confirm that the host supports the appliance format and virtual-hardware requirements listed on the selected release page before importing it.
A server virtualization platform such as vSphere or Hyper-V lets the owner adjust resources and run the VM without a desktop user session. Configure automatic startup after the host restarts. Desktop hypervisors can be useful for a lab, but their startup and availability depend on the host configuration.
Route: Self-managed macOS Server
Follow this route on the dedicated Mac that will run FileWave Server, not on a Mac used only to administer FileWave.
1. Prepare the Mac
- Confirm its macOS version and hardware against the release's Server table, and sign in with a local administrator account. Confirm the agreed storage and backup plan.
- Connect the Mac to the intended server network. For a manually assigned address, open System Settings > Network, select the connection, then Details > TCP/IP. Set Configure IPv4 to Manually and enter the approved IP address, subnet mask, and router. Under DNS, add the approved DNS servers, then save the settings. See Apple's manual IP instructions if your macOS layout differs.
- Confirm correct date, time, and time synchronization, and configure the Mac to remain available for server work rather than sleeping during the evaluation. Keep local access available while changing network or power settings.
- Have the Mac administrator disable IPv6 on the network service used by the Server. First list the services in Terminal:
networksetup -listallnetworkservices
Use the network service name, not a device identifier such as en0. For example, only if the listed service is named Ethernet, the command is:
sudo networksetup -setv6off "Ethernet"
networksetup -getinfo "Ethernet"
Confirm that the reported IPv6 setting is off and that IPv4, router, and DNS connectivity still work. Use the actual service name in both commands. Record the original IPv6 setting before changing it; if access breaks, use local access to restore the recorded network settings and involve the network owner. Do not disable IPv4. FileWave's IPv4 guidance explains why server components use this configuration.
2. Install FileWave Server
- On the 16.4.1 release page, find macOS Downloads and download macOS Server. For this release, the file is
FileWave Server.pkg, a direct PKG download—not a DMG. Do not choose the Client, Booster, or Central package instead. - Open
FileWave Server.pkgon the Server Mac. The installer is signed by FileWave (USA), Inc. Read its introduction/readme and license, continue through the installer, accept the license if authorized, then choose Install and authenticate with the Mac's local administrator credentials. Do not bypass a signature or security warning; stop and check the download with your FileWave contact. - Wait for Installer to report completion. If installation fails, retain the error and installer log for the server owner; do not repeatedly reinstall or run copied Linux installation commands.
- Allow the Server services to finish starting. The 16.4.1 package starts them automatically, with final startup work running asynchronously. An Installer success message alone does not establish that Central can connect. Do not run a second Server installer to try to speed this up.
3. Connect and configure the server name and certificate
Continue to Connect and verify your self-managed Server below. Skip the Debian and Webmin sections. The Mac's local administrator account is not the FileWave application administrator account.
Route: Debian Server appliance
1. Import the Server appliance
From the 16.4.1 release page, download one Server image for your hypervisor:
| Hypervisor | Server download |
|---|---|
| VMware / OVA-compatible platform | FileWave_Server_Debian_16.4.1.ova |
| Microsoft Hyper-V, Generation 2 | FileWave_Server_Debian_16.4.1_hyperv-gen-2_VHD.zip |
- VMware: start the OVF/OVA deployment workflow, select the Server OVA, give the VM an evaluation name, choose its host and datastore, and map its network adapter to the approved server network. Review resources and disk provisioning with the virtualization owner, finish the import, and wait for it to complete before powering on. The VMware import reference illustrates an older vSphere interface; use it for import mechanics, not its IVS-specific closing steps.
- Hyper-V: extract the Server ZIP on the Hyper-V host. In Hyper-V Manager, select the host and choose Action > Import Virtual Machine, select the extracted VM folder, and choose Copy the virtual machine (create a new unique ID) for this new evaluation instance. Complete the import, then open the VM's Settings > Network Adapter and connect it to the approved external virtual switch. If the host cannot read the supplied VM definition, have the virtualization owner use the existing-VHDX method: create a Generation 2 VM, attach the Server disk, and apply the agreed Server resources. Do not copy IVS memory or second-NIC instructions into a Server VM.
- Confirm the VM's resource allocation, connected network, persistent MAC address if using a reservation, and automatic-start behavior. Open the hypervisor console and power on the VM. The appliance already contains FileWave Server; do not run a separate Server installer inside it.
Other lab-hypervisor instructions remain in FileWave Virtual Appliances. Use an x86_64-compatible host for this Debian image; macOS Server support on Apple Silicon does not make the x86_64 appliance an ARM image.
2. Secure the appliance account and give it a stable address
Keep the hypervisor console open throughout setup.
- At the console, sign in to the new appliance as
fwadminusing the factory passwordfilewave. Complete the required password change immediately and store the new password in your organization's approved credential manager. - Test a separate login with the new password before closing the original session. New Debian appliances delivered with 15.5.0 or later disable direct root login; use
fwadminandsudofor administrative work. Existing older appliances do not acquire this account configuration merely because FileWave software is upgraded. Follow First Login and Password Change for those distinctions and failed-login recovery. - Use the console's displayed address, or run the read-only command
ip a, to identify the connected interface's IPv4 address and MAC address. Interface names vary; do not assumeeth0,ens160, orens32. - For the shortest setup, keep the appliance on DHCP and ask the network administrator to reserve the approved address for that MAC address. Confirm the DHCP service supplies the intended subnet, default gateway, and DNS servers. If the reservation changes the current address, arrange a controlled reboot from the hypervisor console after the reservation is in place. Wait for boot to finish and confirm the reserved address at the console.
- Have the DNS administrator point the agreed FQDN's A record to that stable address. Follow the appliance DHCP reference if the appliance receives an unexpected address; another DHCP server or the wrong reservation can be responsible.
No DHCP or no address? Stop before opening Webmin. Ask the network owner to provide temporary approved DHCP access or have the appliance administrator configure a static address from the console. Do not use CentOS nmtui instructions on this Debian appliance. See the command-line note below before using older examples.
The appliance account controls the operating system, SSH, and Webmin. It is separate from the FileWave application account used in Central, even if both are named fwadmin.
3. Review the appliance in Webmin
Webmin is the appliance's browser interface for operating-system settings, not FileWave Central or Anywhere.
- On a trusted administration computer, open the Webmin address shown by the console, using HTTPS and port 10000. If the factory appliance presents a self-signed certificate warning, first match the hostname or IP to the console and confirm that you are on the intended management network. Before entering credentials, have the appliance owner verify the initial certificate or connection through an approved, independent method; an address match alone does not authenticate a self-signed certificate. This initial appliance check is not permission to ignore certificate warnings on device-enrollment services.
- Sign in as
fwadminwith the new password you just set. Do not use the factory password again, and do not changerootas a substitute for securingfwadmin. - Open Webmin > Webmin Configuration > Operating System and Environment and confirm that the detected OS matches the installed Debian release. Do not force the old Debian 12.4 value shown in older instructions onto a Debian 13 appliance. If the detected release is wrong or unsupported by the installed Webmin, stop and ask the appliance owner to resolve it.
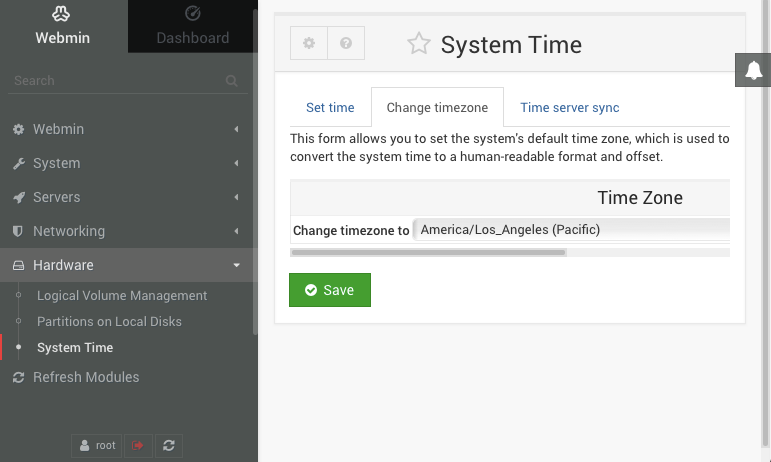
- Under Hardware > System Time, check the timezone and current time. If the timezone needs correction, have the appliance owner use Change timezone and Save. Appliances normally arrive with time synchronization configured; review Time server sync, and have the appliance owner change the source only if your network requires an approved alternative.
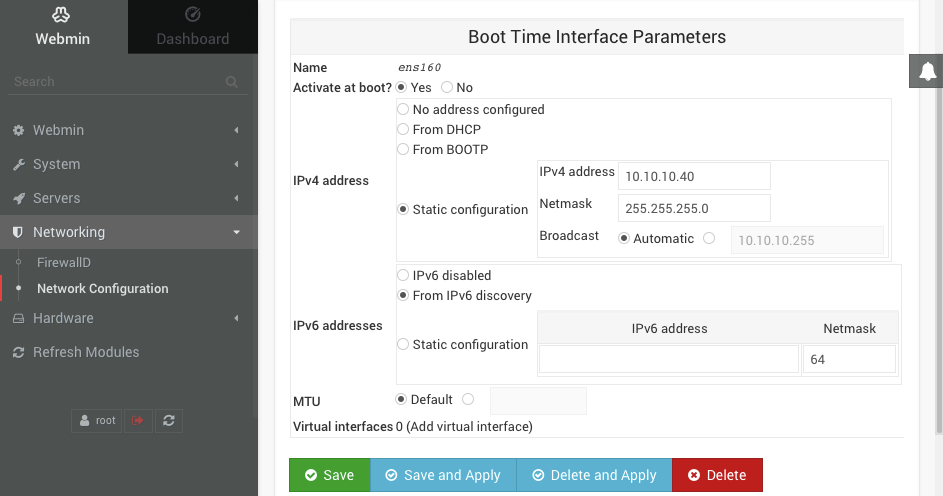
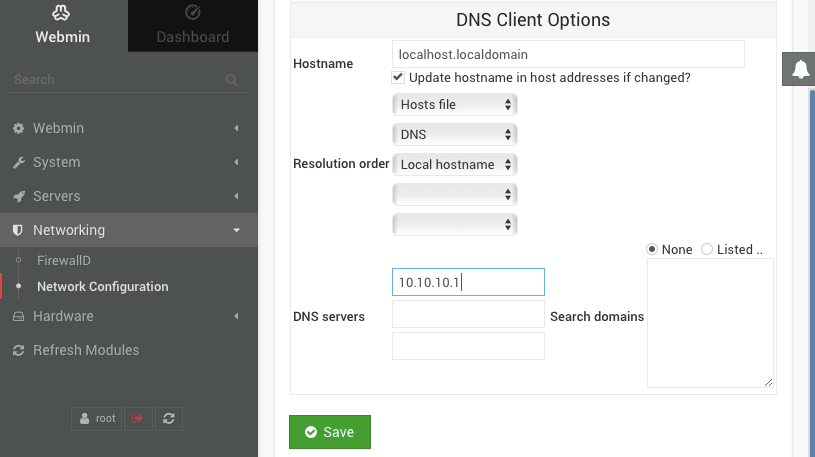
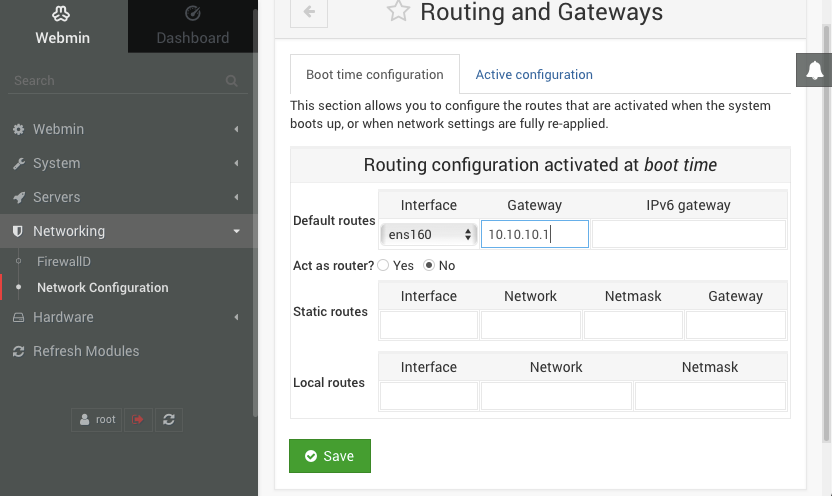
- Under Networking > Network Configuration, review Network Interfaces, Hostname and DNS Client, and Routing and Gateways. Check the connected interface/address, DNS servers, and active default route against the network plan. With a working DHCP reservation, leave the interface on DHCP; you do not also need a static configuration in Webmin.
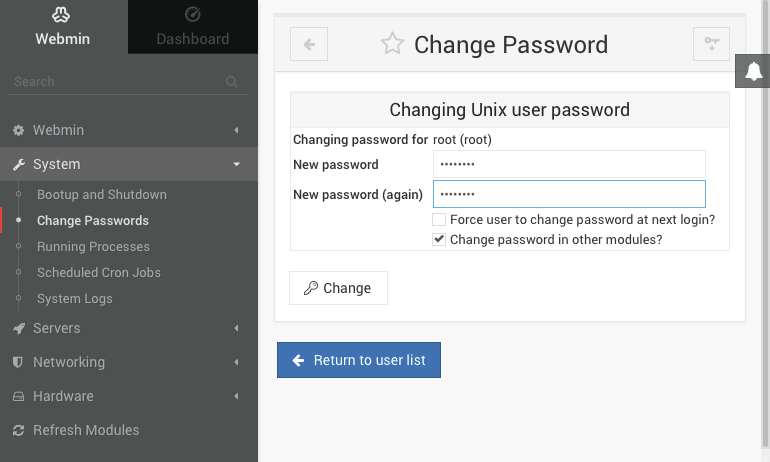
- Confirm that you can sign out and back in with the changed appliance password. For a later password change, use Change a FileWave Appliance Password in Webmin, selecting fwadmin on new 15.5+ appliances.
You can now continue to Connect and verify your self-managed Server. If Webmin is unreachable, first check the console address and access from the management network. Do not change application credentials in Central to fix an appliance-login problem.
Optional: use a manually configured static address instead of a DHCP reservation
Use this alternative only when your network owner requires it and the appliance administrator has confirmed that the persistent interface, DNS, and routing controls described below apply to the installed Webmin version. Have the approved IP, subnet mask, DNS servers, default gateway, console access, and a recoverable pre-change backup ready. Record the original values first. Changing the address can disconnect Webmin and SSH.
In Networking > Network Configuration, configure the actual connected interface under Network Interfaces. In its boot-time settings, select Static configuration, enter the approved address and subnet mask, and save the persistent configuration. Configure the approved DNS servers under Hostname and DNS Client and the default route/interface under Routing and Gateways. Review all three before applying network changes or rebooting. Where separate Save and Save and Apply controls are available, Save stages the interface settings; Save and Apply can interrupt your current session immediately.
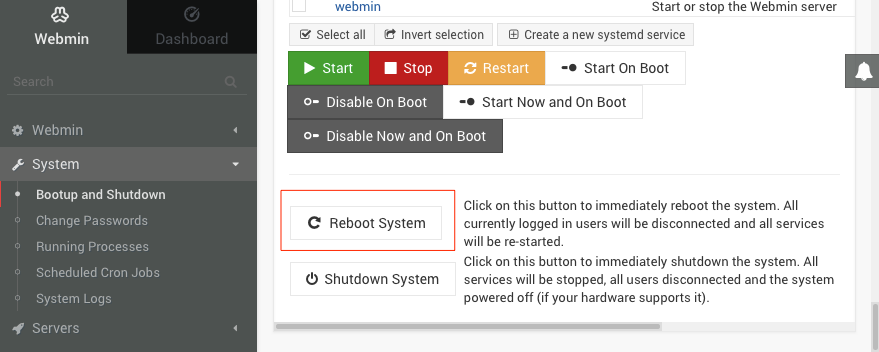
Have the appliance owner apply the completed configuration during the agreed window. If using Webmin's System > Bootup and Shutdown > Reboot System, understand that this restarts the entire appliance and disconnects users; confirm only after checking the saved configuration. Follow boot progress at the hypervisor console, then reopen Webmin at the new address. Verify the address, active default route, and DNS—not just the IP field. If access fails, use the console to restore the recorded settings or the agreed pre-change recovery point before trying again.
The Webmin reference has additional illustrations, but some text still describes older root-account and CentOS workflows. On a new Debian appliance, follow the fwadmin instructions on this page; do not run its nmtui or service network restart example. If your current Webmin does not offer the described persistent-settings controls, stop and have the appliance owner confirm the supported method rather than guessing.
Command-line and older-appliance reference
The static-address command-line reference is for appliances that use /etc/network/interfaces; it is not a universal Debian recipe. Its current example lacks a default gateway and includes a DNS value that is also the example subnet's broadcast address. Do not paste that example into your appliance. A qualified administrator must confirm the networking/resolver configuration in use, back it up, substitute the actual interface and approved addresses, use appropriate privileges, and verify recovery through the console before applying changes. Do not overwrite /etc/resolv.conf or hosts files simply because an older example says to.
For a new evaluation, the DHCP-reservation route above avoids those manual file edits. Existing appliances may retain older login and network settings; consult their owner and the first-login article rather than enabling root or applying new-appliance assumptions. CentOS commands are not part of this Debian route.
Connect and verify your self-managed Server
Both self-managed routes finish here. The server owner performs server-level changes; the network and certificate owners confirm their parts before you enroll devices.
- Connect in Central. Install the matching Central version on an administration computer. Open FileWave Central, enter the agreed FQDN without
https://, leave the main connection port at 20016, and sign in. For a fresh self-managed Server, the initial application credentials arefwadmin/filewave; change that application password immediately after the first successful connection. In Assistants > Manage Administrators, select fwadmin, open User details, choose Set password, enter and confirm a unique password, and save with Apply. Store it securely and verify a new Central login before closing the original session. See Managing FileWave Administrators; if the controls differ in your version, have the server owner complete this step with you before proceeding. Do not use the Mac login or newly changed Debian password. FileWave Central Setup covers installation and first connection. If a certificate prompt appears during initial setup, confirm the Server identity with its owner before trusting it; do not accept an unexplained mismatch. - Set the server name and certificate before enrollment. In Central Preferences > General > SSL Certificate Management, upload the approved
.p12bundle using its password. In Preferences > Enrollment (Mobile in 16.4.0), verify the MDM Server Address uses the same FQDN. Check the actual MDM port against your network plan rather than changing it to match an old screenshot. Follow Name and Certificate Planning for the self-managed local-name resolution and conditional ApacheServerNameconfiguration; its older screenshots label Enrollment as Mobile. The server owner should back up any affected files and coordinate a restart only when that procedure requires it. Certificate preparation is for the certificate owner; do not replace an existing server's identity as a trial exercise. - Verify reachability from the intended networks. Confirm that DNS returns the expected address from the administration computer and each test-device network. Have the network owner check the active default route, DNS service, and the required inbound/outbound connections using the port-testing guidance. A ping, a Webmin login, or a successful IP assignment alone does not prove FileWave services are reachable.
- Check the services you will use. Reconnect Central after any required service restart and confirm that its administration views load. For web-based enrollment in your chosen platform route, open the enrollment URL supplied by your server owner or the chosen platform's setup instructions from the test-device network and verify a valid certificate for the agreed FQDN, without a name, trust, or expiry warning. Do not enroll a device yet. If the address, certificate, or services are wrong, stop and involve their owner before proceeding.
- Record the handoff. Keep the FQDN, Server version, hosting route, stable address, responsible administrators, certificate renewal owner and renewal date, and backup/recovery location in the evaluation notes. Store passwords and private keys only in the approved credential system. Confirm the evaluation license and expiration with your FileWave contact before enrolling devices.
Ready to continue: Central connects to the intended Server, the server name and certificate are correct, and the network checks needed for your chosen platform pass. Continue with Central Preferences, then choose your platform from the Evaluation Guide introduction. Configure only the integrations that platform needs.
If Central cannot connect after installation, check the FQDN, address, version, credentials, and allowed ports with the relevant owner. On macOS, also allow initial service startup to finish and inspect the installation error/log if one was reported. On an appliance, confirm the reserved/static address at the console. Do not make repeated password guesses, reimport a VM, or restart shared services as a first troubleshooting step.
Earlier interface examples
View the retained network and Webmin illustrations
These existing images illustrate earlier interfaces; they do not show the current Debian/Webmin version or prove that settings were saved successfully. Use your own approved addresses and interface names. The root-account images are historical: use fwadmin on new 15.5+ appliances. The IPv6 discovery setting visible in the older network image is not the current FileWave Server recommendation.

No comments to display
With the webmin UI setup, in step 7, if you choose "Save and Apply", I have found that the machine will then be inaccessible via any address, as there is no default gateway. If in this state, it can be solved using the nmtui command in step 1.
It would be better to click "Save" in step 7, continue the rest of the network configuration steps, and have the IP changes applied as part of the step 10 reboot.
In reply to #1
Thanks Matthew. We have made this change and it's a good point.
The Webmin UI configuration guide refers to "nmtui" for network configuration. However, nmtui does not seem to be part of the FileWave .ova image.
In reply to #3
Thanks. Page updated to link to our KB on network configuration for our Appliances.
No comments to display